
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
A featured contribution from Leadership Perspectives, a curated forum for enterprise security leaders, nominated by our subscribers and vetted by the Enterprise Security Magazine Editorial Board.

Formerly Pure Storage
Strategic Security for Measurable Business Impact
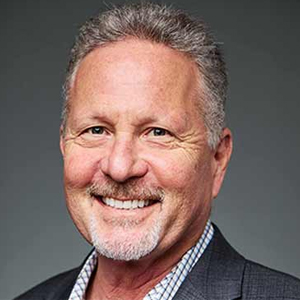
Rick Orloff
Rick Orloff brings investigative discipline and enterprise-scale strategy to his role as Vice President and Chief Information Security Officer at Everpure Storage. He began his career as a licensed private investigator conducting corporate investigations in Silicon Valley before joining Lam Research. He later moved to Apple, where he built and matured multiple products and enterprise security programs.
Building on that foundation, he now leads Everpures global cybersecurity strategy across infrastructure, product security, resiliency, and AI governance, positioning security as a core function and a catalyst for innovation and sustainable growth.
Security Strategy Grounded in Business Risk
At the executive level, security strategy must be anchored in business risk and focused on what is truly meaningful and actionable for the organization.
A completely risk-averse mindset does not strengthen security. It often produces layers of policies and procedures that appear comprehensive but are quietly ignored in practice. That creates bureaucracy rather than a competitive advantage.
Calculated risk is often necessary. When risk tolerance is clearly understood, the security program becomes precise with discipline that allows the organization to move forward without unnecessary friction to the business.
Aligning Security with Growth
Security is not separate from business performance. It is part of it.
In my role, I oversee corporate infrastructure, production, and development systems, DevSecOps practices, the Secure Software Development Lifecycle, business continuity, disaster recovery, incident response, and enterprise resiliency. Central to that mission is a highly capable team with deep expertise and operational rigor.
The modern CISO must extend beyond protection. Security should contribute directly to measurable business growth.
“Security is not separate from business performance. It is part of it.”
We established a dedicated Artificial Intelligence Security pillar supported by defined governance structures and technical controls. This ensures emerging technologies operate within clear risk boundaries while giving leadership visibility into our risk posture and exposure.
Separately, we built a sales enablement pillar measured against defined outcomes. Purposefully structured, security capabilities become a market differentiator, reinforcing customer trust, informing product roadmaps and supporting revenue objectives.
Identity as the Foundation of Zero Trust
Zero Trust begins with identity.
Identity extends beyond usernames and passwords. It includes anything that grants access to anything else, such as tokens, API keys, certificates, domains, service accounts and systems. Each must operate under least privilege.
A disciplined governance structure for identity lifecycle management is essential. Role-based and attribute-based access controls ensure individuals and systems have access limited to what they need to perform their functions.
A mature Zero Trust program requires governance, enforcement, monitoring and alerting. One overlooked risk is posture drift. Controls are deployed for a business outcome, then modified over time without sufficient rigor, eroding effectiveness.
Sustaining Zero Trust requires the same oversight discipline as deployment.
Guardrails That Enable Agility
I often describe security through a guardrail analogy.
Imagine the organization operating within a swim lane. The guardrail on the left represents governance, risk, and compliance. It ensures the business operates with rigor, maintains separation of duties, and drives certifications that support sales enablement. The guardrail on the right represents pragmatic technical security controls aligned to intended outcomes.
Within those boundaries, engineering and the broader business can move as quickly as they choose. Security owns the rails, not the business velocity.
This approach is particularly important in product development. Security requirements must be defined during ideation and embedded early in the lifecycle. When introduced late, they become reactive, inefficient, and less effective.
A disciplined process ensures stakeholder engagement and security by design.
Driving Security Through Complete Visibility
Effectiveness starts with 100 percent visibility into the enterprise, eliminating blind spots.
If we deploy a secrets management initiative, I ask: Are we scanning one hundred percent of our infrastructure for secrets exposure? If not, the program is incomplete.
Partial coverage creates blind spots and false assurances to the Board of Directors. If a control does not provide full visibility into its intended scope, we remove the obstacles preventing that coverage.
True effectiveness starts with complete awareness.
AI as a Force Multiplier in Security
AI is one of the most powerful tools available to security teams.
In cybersecurity, time is an adversary. The longer vulnerabilities remain open, the greater the exposure. AI compresses that timeline by accelerating detection and potential exploitation.
At the same time, AI magnifies the importance of identity governance. These systems operate through identities to access data and execute actions. If identity frameworks are overly permissive, AI amplifies exposure at scale. As autonomy increases, the frameworks defining what systems can access and execute become increasingly critical.
The importance of security required in the design phase has never been greater.
Resilience Proven Through Execution
Resilience begins by identifying mission-critical business functions and asking a fundamental question: If the primary environment fails, what is our plan for continuity of care and service?
Backup alone does not equal resilience.
Unless the organization has tested the ability to restore backups in an alternate environment and successfully run the business function, it has data, not operational continuity.
To measure resilience, teams should restore backups at a new location and demonstrate that the function operates as intended. Dependencies such as identity configurations, network routes, and system integrations often surface only during restoration. The worst time to discover those gaps is during an incident.
Resilience is proven through execution testing, not just planning documents.
Security at the Governance Level
An important evolution is occurring at the board level. Increasingly, boards recognize the necessity of cybersecurity expertise within their composition.
As exposure windows shrink and blast radius expands, governance-level oversight becomes critical. Organizations benefit from directors who understand governance, risk, and compliance as well as operational security realities.
Security is no longer purely operational. It is strategic oversight.
Owning Security at the Executive Level
Delivering meaningful security outcomes begins with stakeholder engagement. This is not about seeking approval to perform responsibilities. It is about establishing credibility with executive leadership and the board by communicating in terms of business risk and value.
A high-performing global security program delivers disciplined governance supported with pragmatic technical capabilities. If processes or tools do not directly contribute to business-aligned outcomes, they often become bureaucracy that has outlived its intended purpose.
Security leadership means maintaining disciplined boundaries while enabling the business to move confidently. When that balance is achieved, innovation accelerates, resilience strengthens and security becomes a strategic advantage.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
